ABOUT METIS GRC
Risk, compliance and security advice that makes sense for your business
Metis GRC is a UK governance, risk and compliance consultancy, specialising in cyber and information security. We help mid-sized organisations that hold sensitive information manage their risks and meet their obligations, without the cost of a dedicated in-house team.
WHY METIS GRC
How we work
We combine recognised governance, risk and compliance frameworks with years of experience helping large organisations bring their people through change. The result is advice that works in practice as well as on paper, because it’s built around how your business operates.
Plain English, always
No walls of jargon. Every recommendation comes with the reason behind it, written for the people who have to act on it.
Proportionate, not padded
Advice sized to your business, your risks and your budget. Practical frameworks that fit how you work, not a corporate template.
Qualified and independent
IWe bring over a decade of experience across government, technology and regulated sectors, legal and investigative expertise, and ISO/IEC 27001 Lead Implementer and recognised cyber security qualifications. Our advice is independent, with no products to sell you.
Personable and precise
Risk and compliance can feel daunting. We keep things approachable and collaborative, so you feel comfortable asking anything, while bringing the rigour you'd expect from a specialist.
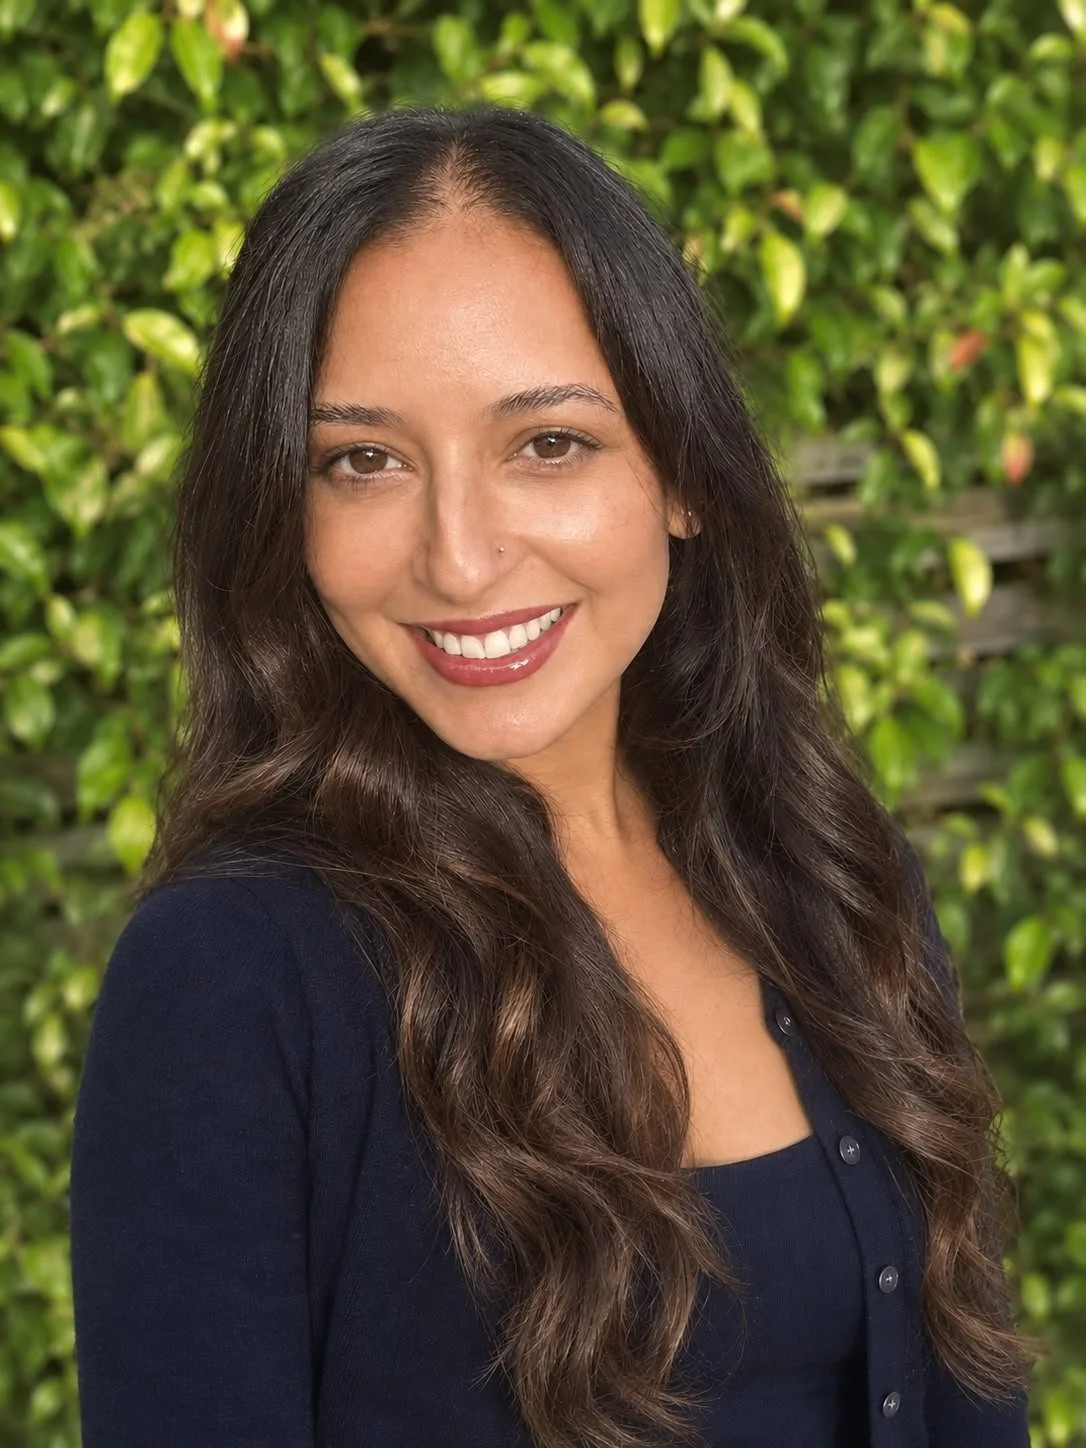
Aliya Beale
Governance, risk and compliance consultant
Aliya founded Metis to bring together what she has spent her career doing: holding organisations to high standards, and helping their people meet them.
A law graduate, Aliya began her career as a Lead Investigator at the Independent Police Complaints Commission (now the IOPC). There she followed the evidence, asked the uncomfortable questions, and wrote findings police forces and their officers could act on. She later became a Training Manager, supporting trainee investigators through to professional accreditation.
She went on to hold senior leadership roles in government, leading learning and development, communications and change at the Cabinet Office, including creating professional standards adopted across government. Aliya then joined the private sector, first in regulated healthcare and then in tech, advising executive teams and leading organisation-wide change, security awareness initiatives and communications through major cyber incidents. Throughout, her focus has been the same: helping organisations meet high standards, bring their people with them, and stand up to internal and external scrutiny.
Now a governance, risk and compliance specialist and ISO/IEC 27001 Lead Implementer, certified in cyber and information security, Aliya combines a legal grounding, an investigator’s eye for evidence and a deep understanding of how people and organisations work. She’s known for staying calm under pressure and moving at pace, and the result is advice that fits your business, training that engages your team, and policies people actually follow.
Our Director
Ready to chat?
Get in touch. Fill in a few details below and we'll get back to you within two business days.